airescues / claude / Claude hub

Claude by Anthropic

Leaked Anthropic API key: revoke it, then check what it spent

Whoever uses your API key spends on your account, so a leaked key is a billing problem as much as a security one. Revoke first, look second.

Revoke

  • Suspect a compromise? Revoke the key immediately.
  • Console API keys page → the key’s menu → Delete API key.
  • The page lives at platform.claude.com/settings/keys in the Claude Console.

Revoke before you investigate: every request made with the key while you look is billed to you.

Why a leaked Anthropic key is a billing problem

  • Anyone who obtains and uses your API key incurs charges on your behalf.
  • Spend limits and rate limits are the safeguard against unexpected usage from leaked keys or errant scripts.
  • Checking the Logs page and the Usage page regularly is how you notice usage that isn’t yours.

Check the damage

  • Charges from a leaked key land on your account.
  • Review the Logs and Usage pages.
  • Spend and rate limits act as a safeguard against leaked keys.
  • Still suspicious? Contact Support.
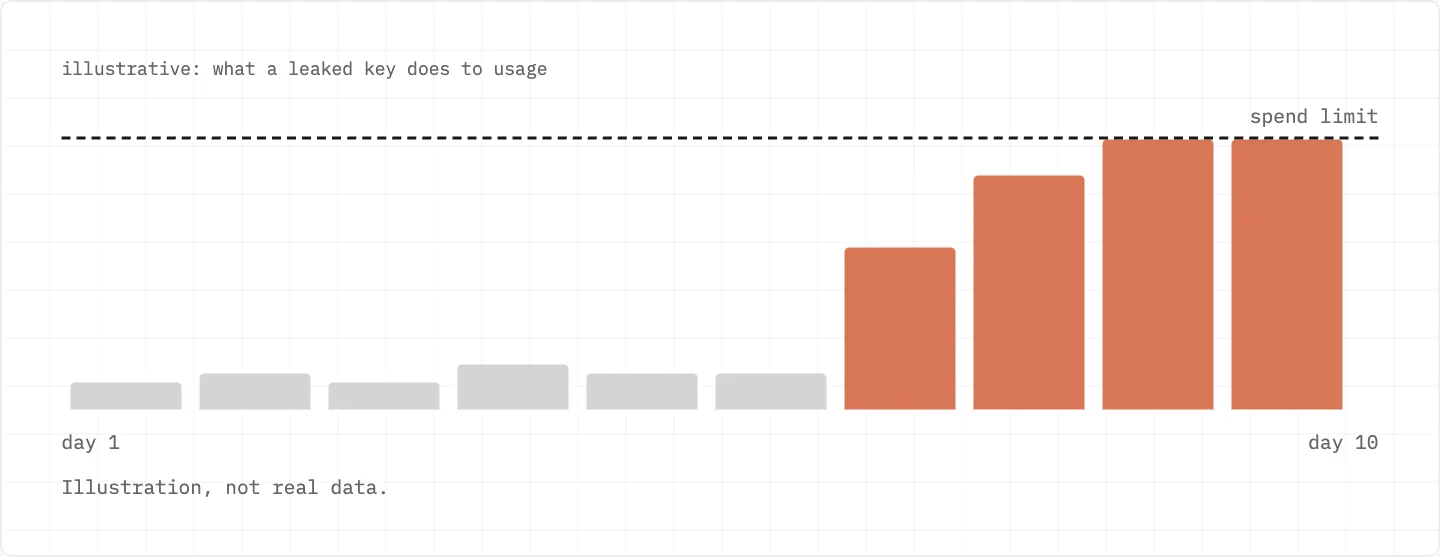
An illustrative bar chart of daily API usage: steady low bars, then tall bars after a key leaks, with a dashed spend-limit line that caps the damage; whoever uses the key spends on your account.
Whoever holds your key spends on your account; spend limits cap how far a leak can go. Illustrative numbers.

Found in a public GitHub repo

  • Anthropic deactivates the exposed key automatically.
  • The owner gets a detailed email notification about the incident.
  • A deactivated key still deserves a look at Logs and Usage for what it did before it was switched off.

Open the Console yourself rather than through a link in a message: that way you know the page is the real one.

API keys, Claude Code tokens and your Claude login are separate locks

  1. Your Claude account and your Console account are separate accounts, even with the same email.
  2. The Console has no password either; an organization with SSO sends you to its SSO provider at login.
  3. Log out of all sessions, in Settings → Account on the web, signs out Claude Code, including setup-token CI tokens.
  4. It does not affect API keys — a leaked key has to be revoked in the Console.

Match the fix to what leaked: a Console key is revoked on the API keys page, a Claude Code or CI sign-in ends with Log out of all sessions.

Reporting a leaked key to Anthropic Support

  • Still seeing suspicious API activity after revoking, or other concerns? Contact Support.
  • Support works in writing, through the messenger and email — there is no phone line.
  • Not the Console owner? Your Primary Owner, Owner or Console Admin can reach out on your behalf.
  • Keep one conversation for the incident rather than opening several.
  • Describe what you saw and when, but leave the key itself out of the message — even one to Anthropic.
  • Every reply appears in the messenger and is emailed to the address on your account.
never paste a key Don’t put an API key in emails or support tickets — not even to Anthropic.

Next for Claude

Sources — Anthropic help pages, checked October 2026

AIRescues explains the official ways back into your own AI account. We are not ChatGPT, Claude, Gemini, Grok or DeepSeek and cannot open any account for you.

Facts are checked against each platform’s help pages; every guide shows the month it was checked.

How we check About Responsible use